Reply to: tickets(326879)
Replies for tickets on suppota
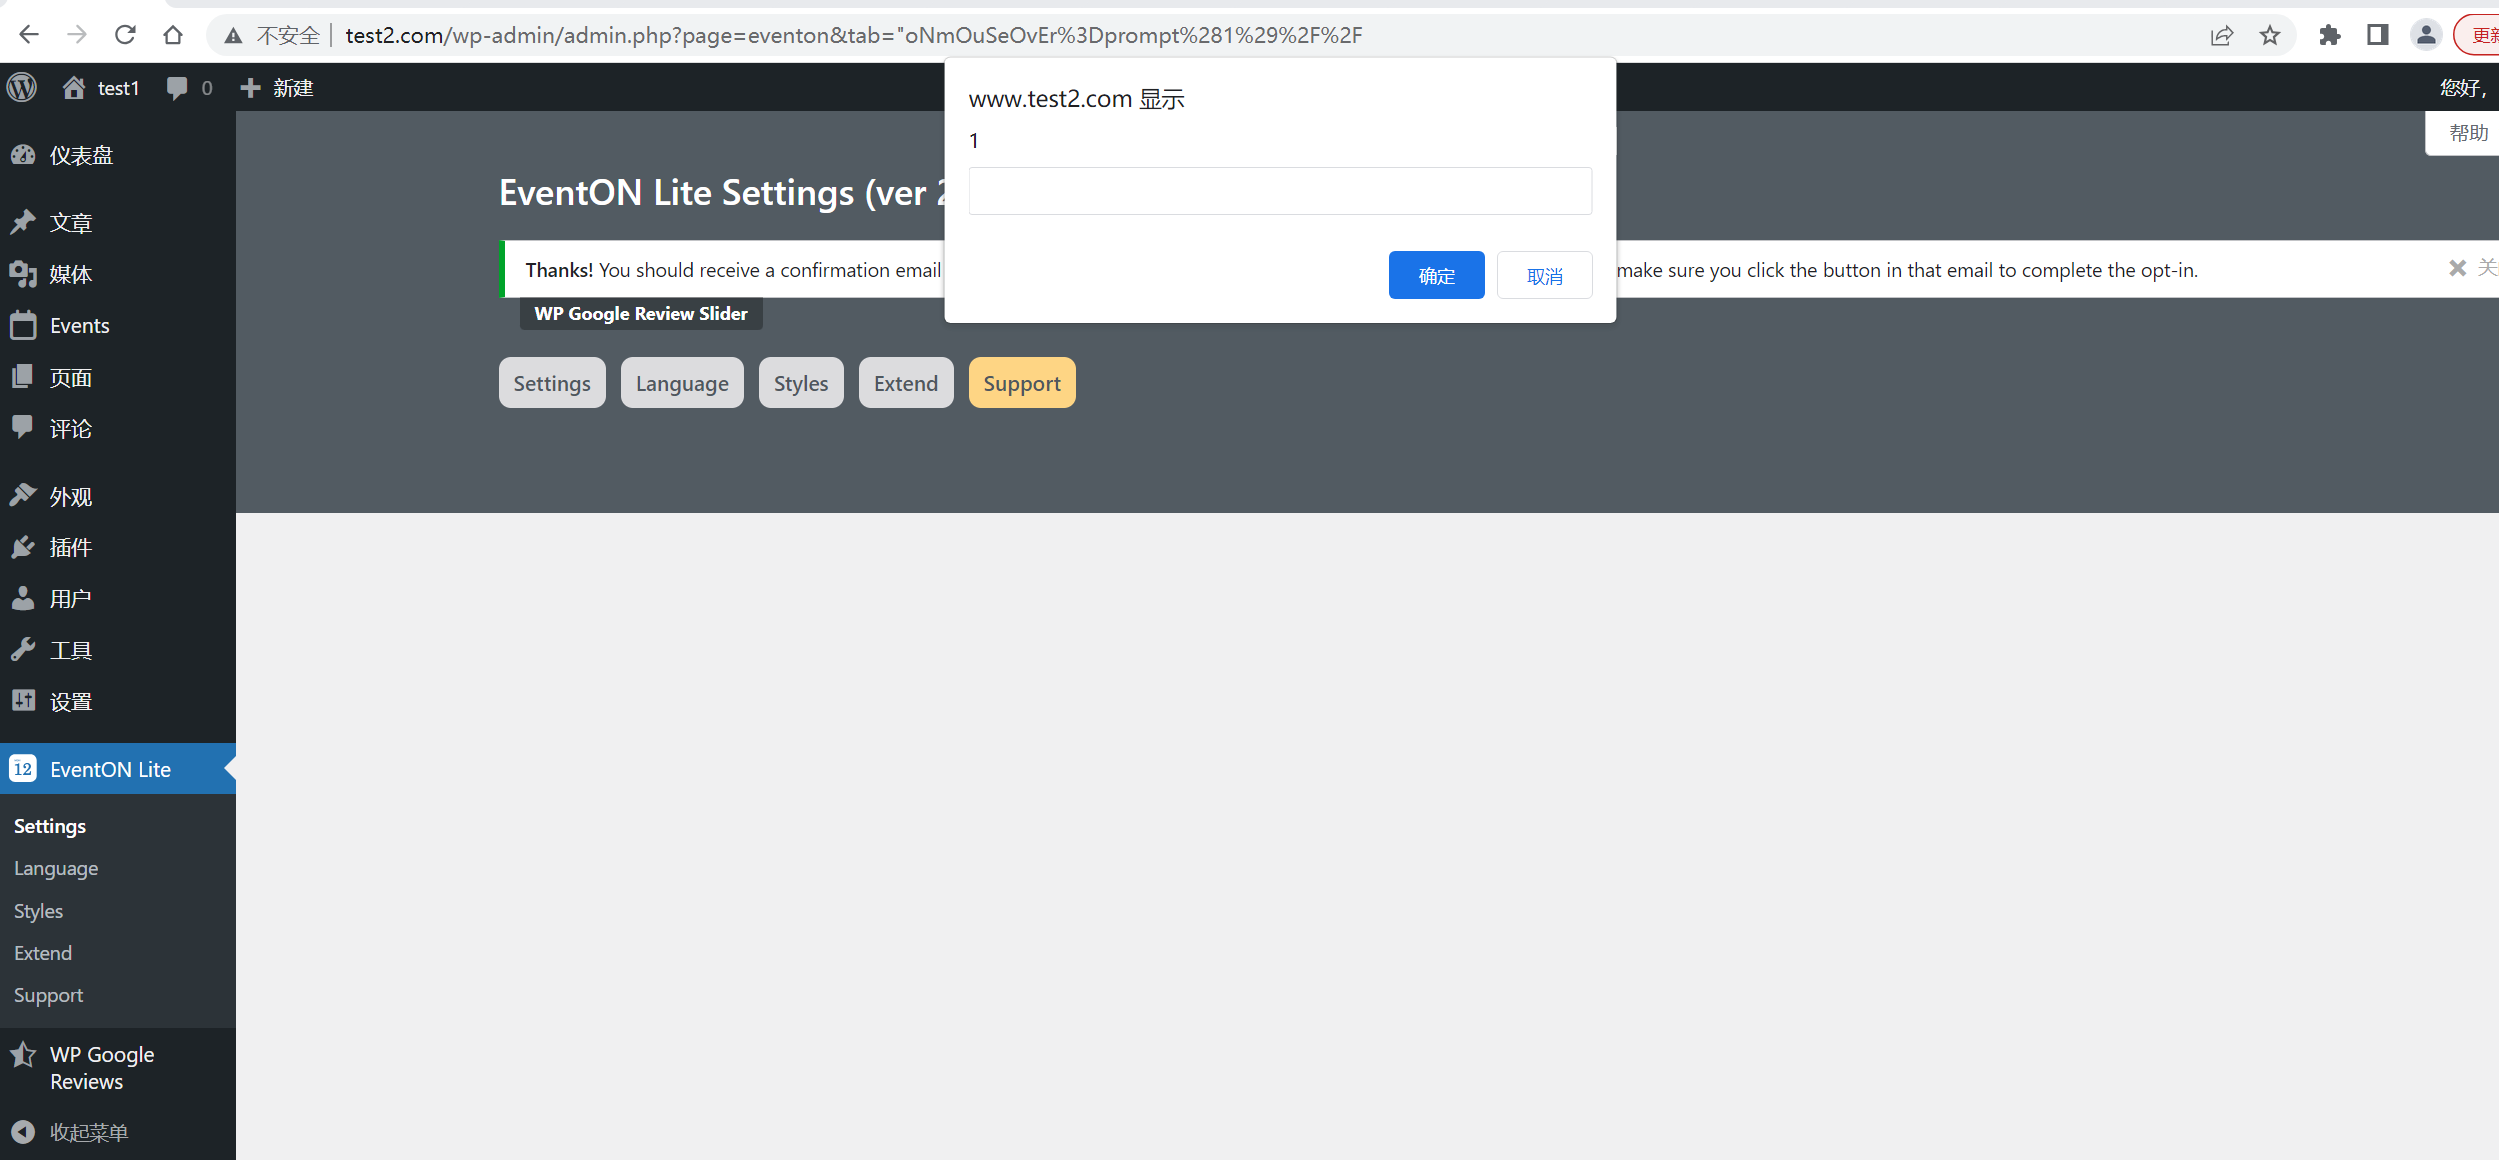
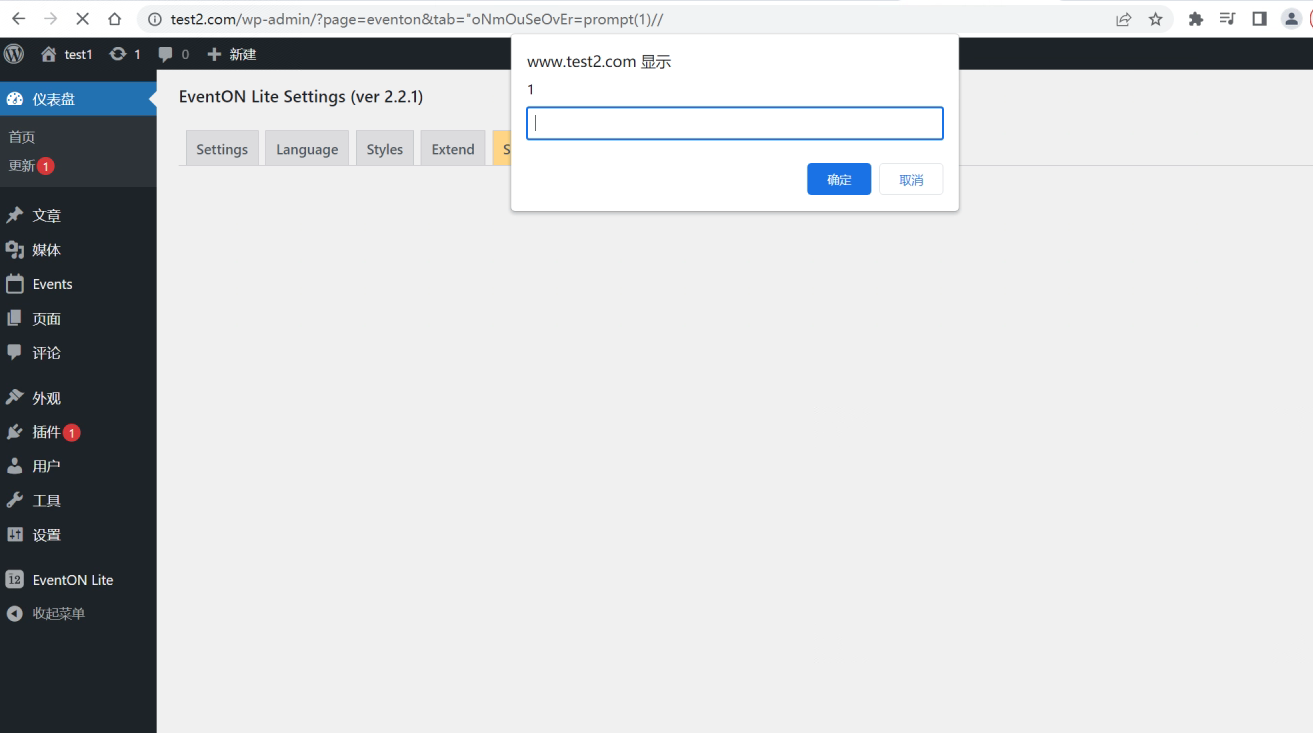
I just tested on the latest version 2.2.1 of the plugin and it appears that it is still vulnerable.I found that the security issue still exists,The Proof of Concept of this vulnerability can be found on here: https://github.com/xsn1210/vul/blob/main/xss%5BEventON%5D%20.md
Description :Download the EventON Lite plugin from the WordPress official website and install the latest version of the EventON Lite plugin. This plugin has an XSS vulnerability, that is, a cross-site scripting attack. The attacker will insert malicious JavaScript code into the web page (input form, URL, message board, etc.), and the payload is ” oNmOuSeOvEr=prompt(1)//, replace the tab parameter in the url of /wp-admin/?page=eventon&tab=evcal_1 with the payload, which will trigger when the administrator/user visits, so as to achieve the purpose of the attack. The essential reason is that the server The data submitted by the user is not strictly filtered, causing the browser to treat the user’s input as JS code and directly return it to the client for execution. What appears here is reflected XSS. Attackers can steal administrators, etc. by using reflected cross-site scripting attacks. User cookies, stealing clipboard content, changing web page content (eg download links), etc.
https://github.com/xsn1210/vul/blob/main/xss%5BEventON%5D%20.md
Navigate to the URL: /wp-admin/admin.php? page=eventon&tab=evcal_1 or /wp-admin/admin.php? page=eventon&tab=evcal_2 or /wp-admin/admin.php? page=eventon&tab=evcal_3 or /wp-admin/admin.php? page=eventon&tab=evcal_4 or /wp-admin/admin.php? page=eventon&tab=evcal_5 and other pages
Change the value of tab to “oNmOuSeOvEr=prompt(1)//, and send the modified url. /wp-admin/admin.php?page=eventon&tab=”oNmOuSeOvEr=prompt(1)//
Or change the value of the argument tab to “oNmOuSeOvEr=alert(document.cookie)// and send the modified url. /wp-admin/admin.php? page=eventon&tab=”oNmOuSeOvEr=alert(document.cookie)//
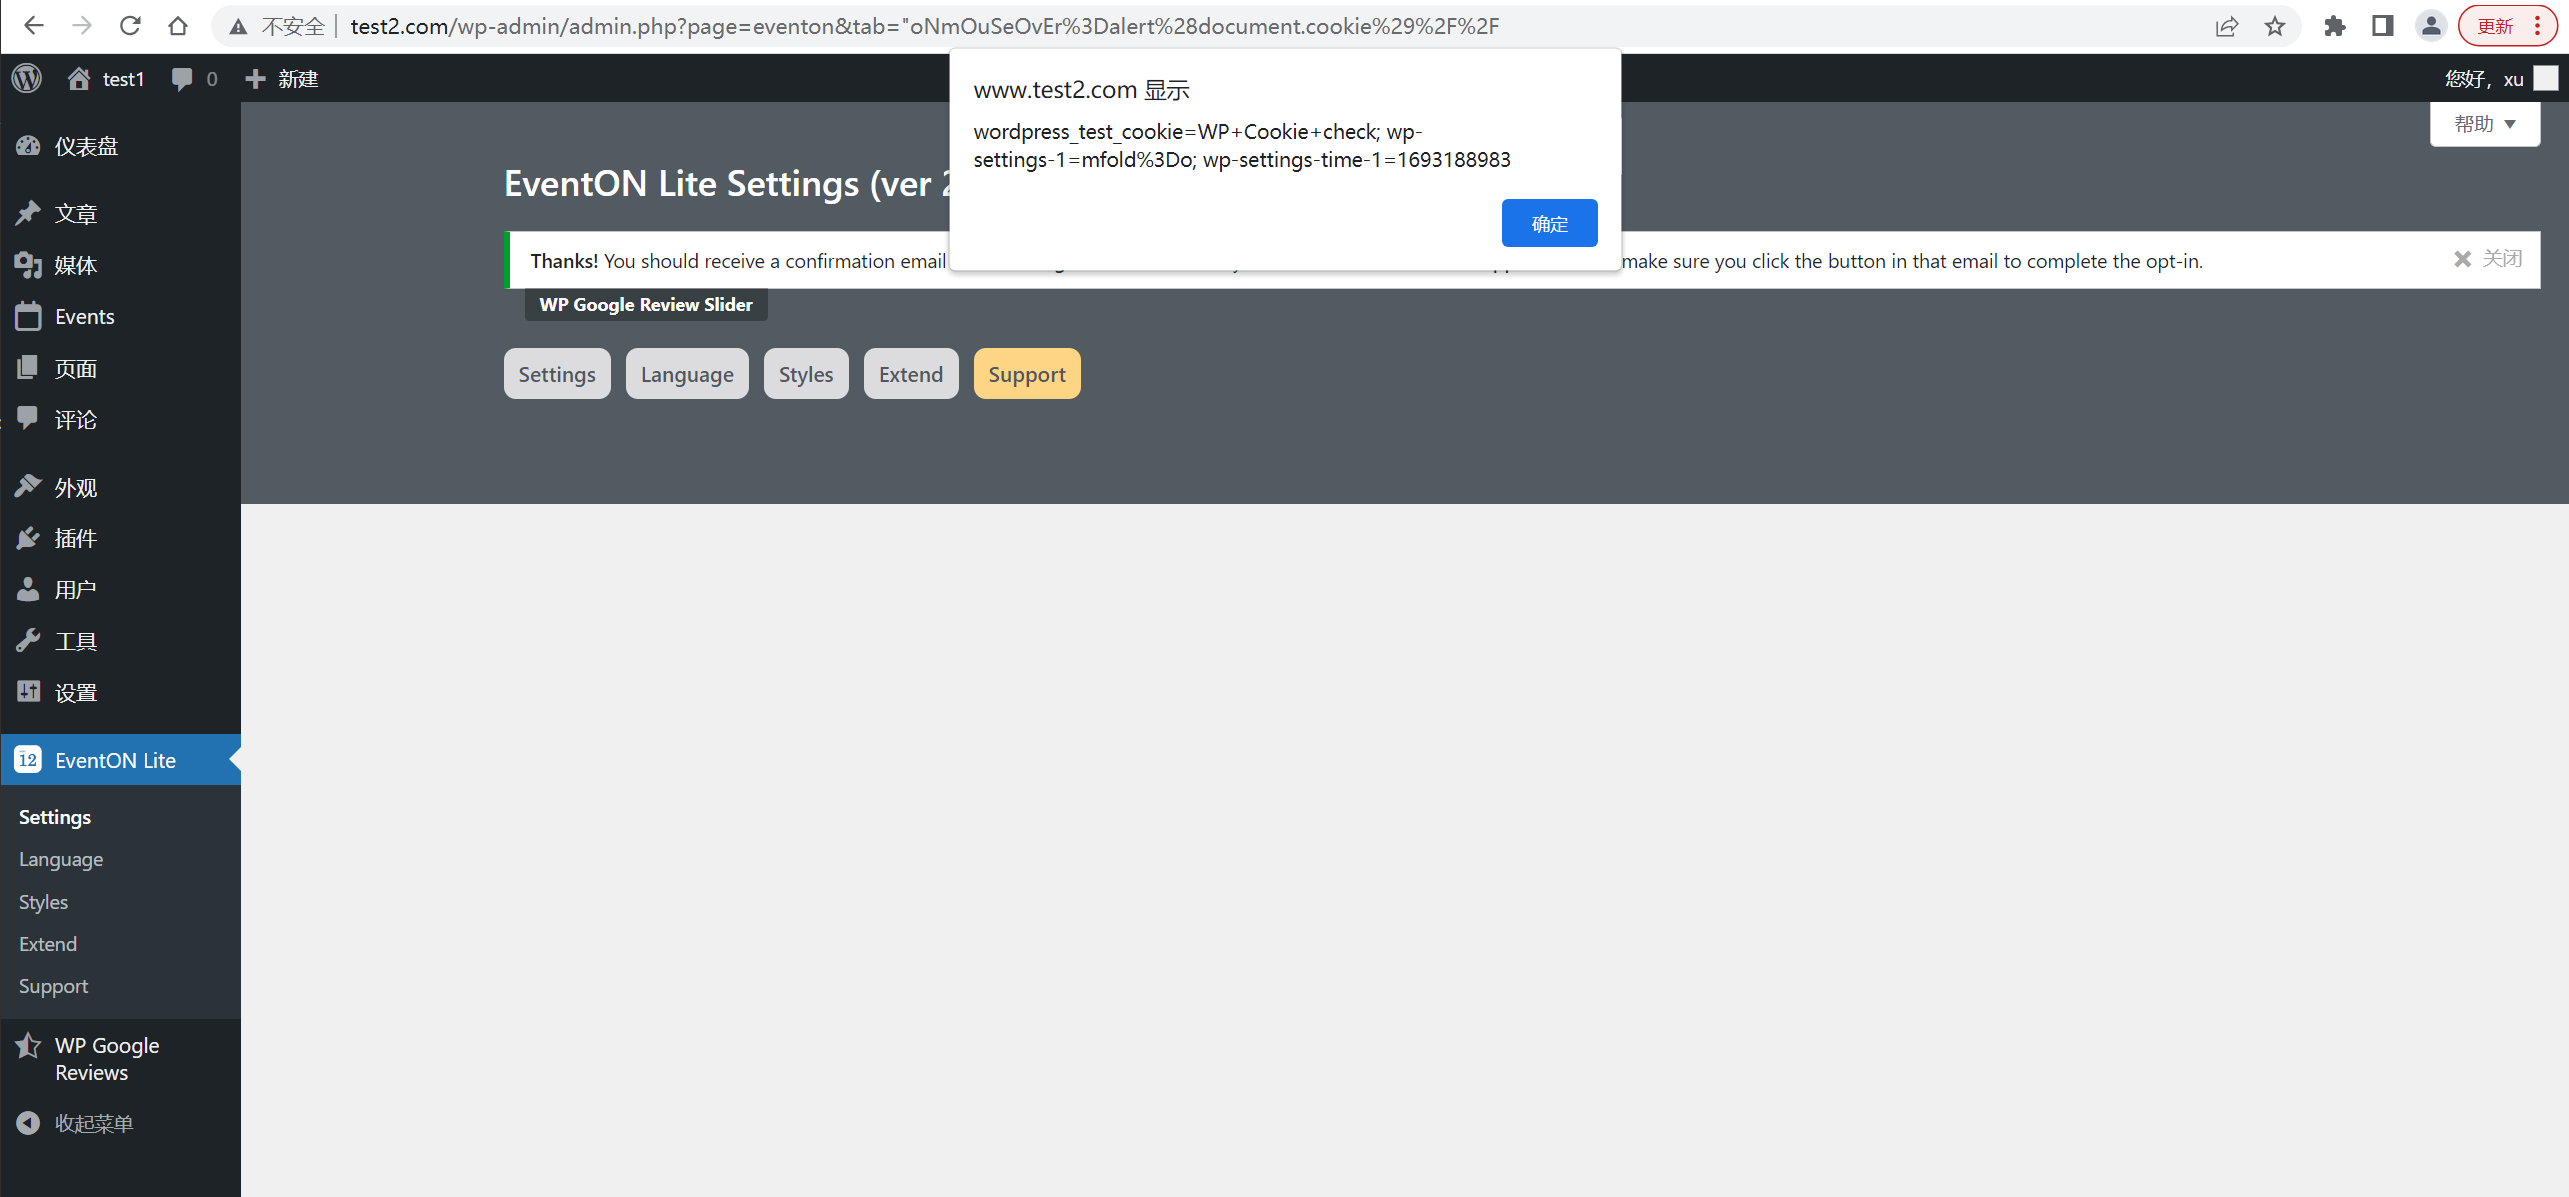
A pop-up window will appear on the web page, and an alarm box showing 1 will pop up, triggering XSS, indicating that there is cross-site vulnerability, recording the vulnerability, and stopping the test.
I’m pretty sure this security issue is recurring in the latest version 2.2.1 of eventON, please fix it as soon as possible.
Good day
I installed the new update of EventOn and was a little disappointed that no problem was solved for me. Can you tell me why. Below again the problems that are still not solved.
Best regards, Juergen
1.
In the single page view, the appointment block is not exactly aligned. It is too close to the edge (see picture).
With kind regards, Jürgen
2.
A question because of the two identical links that are inserted when creating an appointment from the EventOn. Is it not possible to disable the links so that the user does not get to the single page view. It makes especially no sense if you have deactivated the linking to the single page view for the Top Event for example…. Best regards Jürgen
you got me 🙂 im not a professional .. I thought in the picture it mean delete this file. hehe
I put it back in and everything is working! Thank you very much .. im looking forward to add some more functions in the future.
Peace Marc
As it is a multi-site, it is enabled on the Network Admin – but will require a different login for you:
Username: eventon
Password: 2HSYXzuMDKCy8hD8brW%qigi
Let me know if you need anything else to help debug.
amklassiek.nl as a host name should work when you are on a ftp protocol.
Hello,
I added Ticket Box section here:
https://balanzrock.net/wp-admin/admin.php?page=eventon&nginx_helper_action=done&nginx_helper_urls=all&_wpnonce=b49c665323#evcal_004b
So it should be visible now. Please check and let me know.
Please make sure to click on “APPLIQUER LES FILTRES“. Here’s filtered results with only “COMÉDIE”: